Biometric Pathways Unlocked: Authentication Flows for Mobile Slots in Britain's Regulated Gaming Scene
Written by Wendy Keller · Jul 12, 2026
Biometric Pathways Unlocked: Authentication Flows for Mobile Slots in Britain's Regulated Gaming Scene
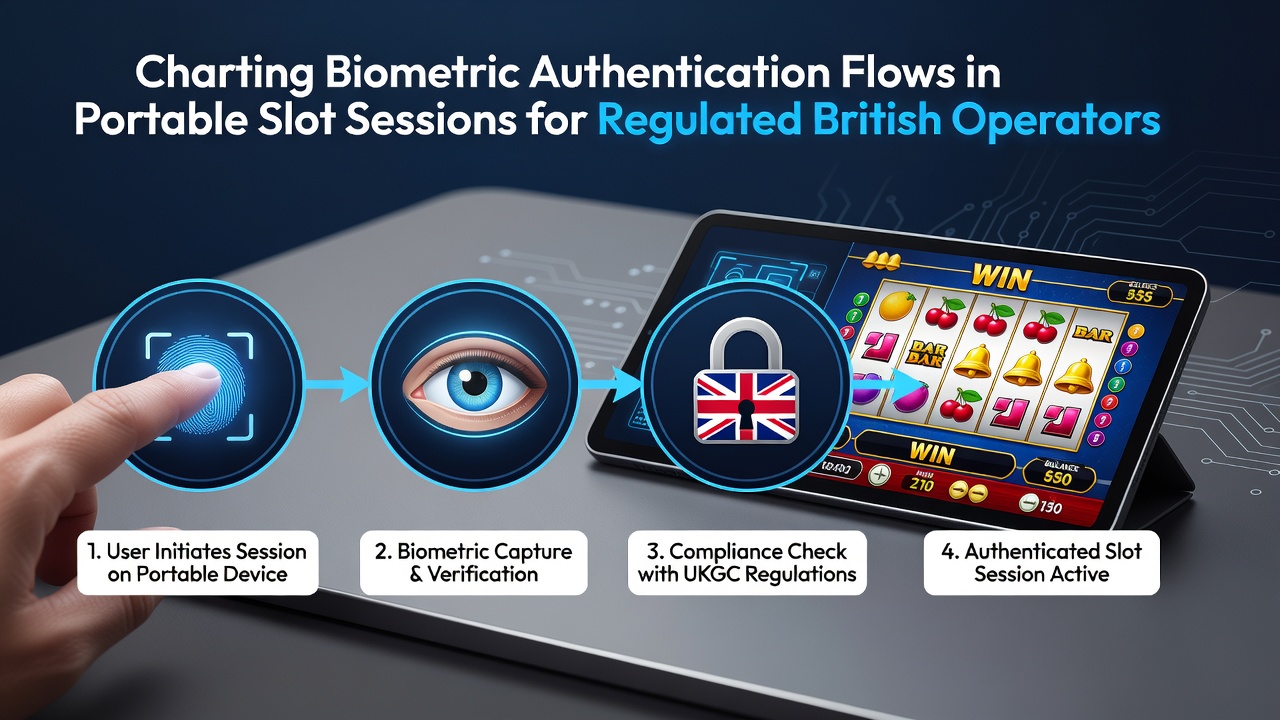
Portable slot sessions on regulated British platforms now incorporate layered biometric authentication sequences that map directly onto device sensors and operator servers, creating streamlined yet secure entry points for players who launch games on smartphones and tablets. These flows typically begin with device-level prompts for fingerprint or facial recognition data, which then transmit encrypted templates to backend systems for verification before any wagering interface activates. Researchers have documented how such sequences reduce friction compared to traditional PIN or password methods while maintaining compliance with data protection standards that apply across licensed operations.
Core Elements in Mobile Biometric Sequences
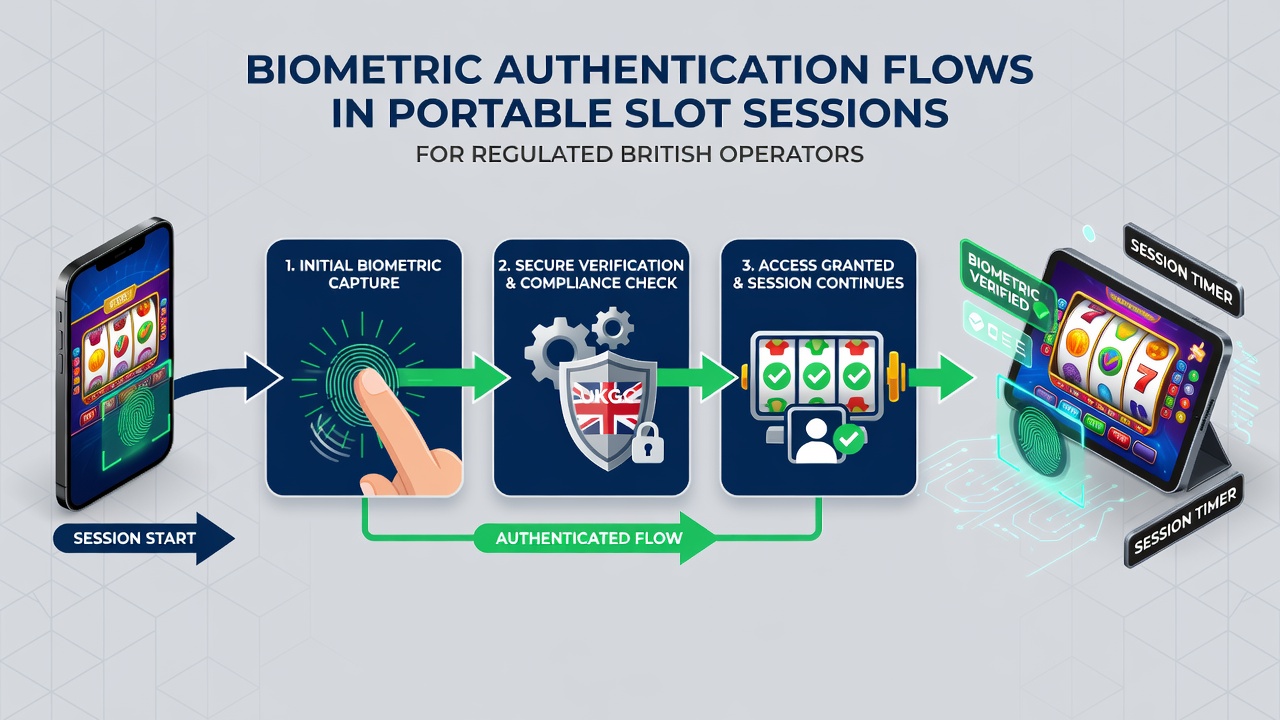
Operators structure these authentication flows around three primary stages that connect user devices to central platforms. Initial capture happens through native hardware like capacitive fingerprint readers or infrared facial scanners on modern phones, after which the system generates a one-way hash that travels via secure channels. Verification follows as servers compare incoming hashes against stored records, granting session access only when matches align within predefined tolerance thresholds. Session persistence then relies on continuous monitoring that rechecks biometric signals at intervals or upon game switches, ensuring ongoing player identity without repeated full scans. Data from industry analyses shows these stages integrate with payment gateways and game engines so that slot spins commence only after successful passage through all checkpoints.
What's interesting involves the way portable sessions handle interruptions such as app backgrounding or network shifts. Systems automatically trigger partial re-authentication using cached tokens combined with fresh biometric samples, which prevents unauthorized handovers while preserving play continuity. Observers note that July 2026 timelines for broader digital identity standards may further standardize these interruption protocols across European markets, drawing on frameworks already tested in Australian and Canadian jurisdictions.
Integration Patterns Across Licensed Platforms
British operators deploy biometric flows in patterns that vary by provider infrastructure yet converge on common principles of encryption and audit logging. Some platforms embed facial recognition as the default for high-value sessions, routing data through on-device processing before any transmission occurs, whereas others prioritize fingerprint for faster throughput during frequent short sessions. Studies from academic sources indicate that hybrid models combining both modalities achieve lower false rejection rates, particularly when players switch between portrait and landscape orientations during slot play.
One study revealed that integration with live dealer elements in hybrid mobile environments requires additional checkpoint layers, where biometric confirmation gates entry to shared tables or bonus rounds. Those who've examined operational logs find that these extra steps maintain separation between slot-specific and table-specific authentication tokens, reducing cross-contamination risks. External frameworks such as those outlined in NIST biometric guidelines provide reference architectures that British developers adapt for local device ecosystems.
Technical Challenges and Mitigation Strategies
Environmental variables like lighting changes or device wear affect facial and fingerprint accuracy in portable settings, prompting operators to implement fallback mechanisms that route users to secondary methods without full session reset. Engineers address template storage concerns by keeping biometric data localized on devices whenever possible, transmitting only verification outcomes rather than raw images. Research indicates this approach aligns with emerging cross-border data rules seen in EU and North American regulations, minimizing exposure during transit.
Performance metrics collected from deployed systems demonstrate that average authentication completion times hover under two seconds for fingerprint flows and three seconds for facial ones when network conditions remain stable. Yet spikes occur during peak hours, leading some operators to deploy edge computing nodes that handle initial hash comparisons closer to the user. Those monitoring these patterns report that such adjustments sustain session fluidity even as slot libraries expand with new titles requiring distinct permission checks.
Comparative Approaches in Global Markets
British implementations draw contrasts with systems operating under different regulatory umbrellas, such as those managed by state bodies in the United States or provincial authorities in Canada. Where American platforms often emphasize multi-factor layering that includes location verification alongside biometrics, Canadian operators have explored voice pattern recognition as an additional portable option for tablet users. Reports from the Responsible Gambling Council highlight how these regional variations influence session abandonment rates, with biometric simplicity correlating to higher retention in mobile slot environments.
Academic papers on mobile security further compare encryption standards, noting that British platforms frequently adopt protocols refined from earlier pilots in Asian markets. These comparisons reveal consistent emphasis on audit trails that log every biometric match attempt, supporting dispute resolution and system refinement over time.
Conclusion
Biometric authentication flows continue to evolve within portable slot sessions offered by regulated British operators, mapping device capabilities onto secure server interactions that prioritize both access speed and identity assurance. As technical standards advance toward 2026 benchmarks, these sequences stand to incorporate refined tolerance algorithms and broader device compatibility, all while drawing lessons from international implementations that have already tested similar architectures. The resulting frameworks deliver measurable improvements in session management without compromising the core requirements of licensed environments.